
Historical security advisories
The 2016 and 2017 advisories, preserved with their original affected-version context.
A reference from an earlier chapter
This material preserves the original Textual documentation and may describe older versions, former services, or superseded policies. It is not a statement of current availability or new Blendbyte commitments.
On this page
These reports concern earlier releases. Use the current supported download rather than following an old emergency workaround on a modern installation. Code examples are shown as text.
Security Advisory: January 2016, #1
Summary
A vulnerability was discovered that allowed JavaScript to be injected into the HTML view that renders channel content.
Codeux Software is not aware of any case in which this vulnerability was abused in the wild.
Details
The vulnerability, which was discovered by Wladimir Palant, has existed since version 2.1.1 (mid-2012) of Textual.
Double quotes (") are allowed to appear inside a URL which means a person with malicious intent had the power to append code to the HTML anchor element which is used to turn a URL into a link.
The vulnerability was fixed by appropriately escaping the characters inside each URL.
Proof of Concept
This web page will be displayed to anyone who hovers their mouse pointer over the URL displayed below.
https://bing.com/#"onmouseover="eval(atob('d2luZG93LmxvY2F0aW9uPSdodHRwczovL2hlbHAuY29kZXV4LmNvbS90ZXh0dWFsL1NlY3VyaXR5LUFkdmlzb3J5LUphbnVhcnktMjAxNi0xLmtiJzs='))
This works by decoding the encoded data and evaluating it as JavaScript.
The encoded data, when decoded, is:
window.location='https://textualapp.com/docs/legacy/security/advisories';
Security Advisory: October 2017, #1
Overview
Users that are running version 7.0.5 of Textual or an earlier version are advised to update to version 7.0.6 immediately.
Your personal information is NOT at risk. The bug that was patched by version 7.0.6 caused users to be banned from servers for unintentional private message spam. That is the worst that can happen.
This is a preliminary advisory. More information will be available at a later date.
Standalone Version
If you are running the standalone version of Textual, then follow these steps to update:
-
Navigate to the main menu in the top left corner of your screen
-
Click the bold menu labeled “Textual” next to the Apple symbol ()
-
In the menu that appears, click “Check for updates…”
Mac App Store Version
If you are running the Mac App Store version of Textual, then see the Updates section of the store.
Hidden Preference
If you are unable to update to version 7.0.6 of Textual, then you can permanently disable the Off-the-Record (OTR) Messaging feature to work around the bug.
To disable this feature, follow these steps:
- Open the application named Terminal using Spotlight.
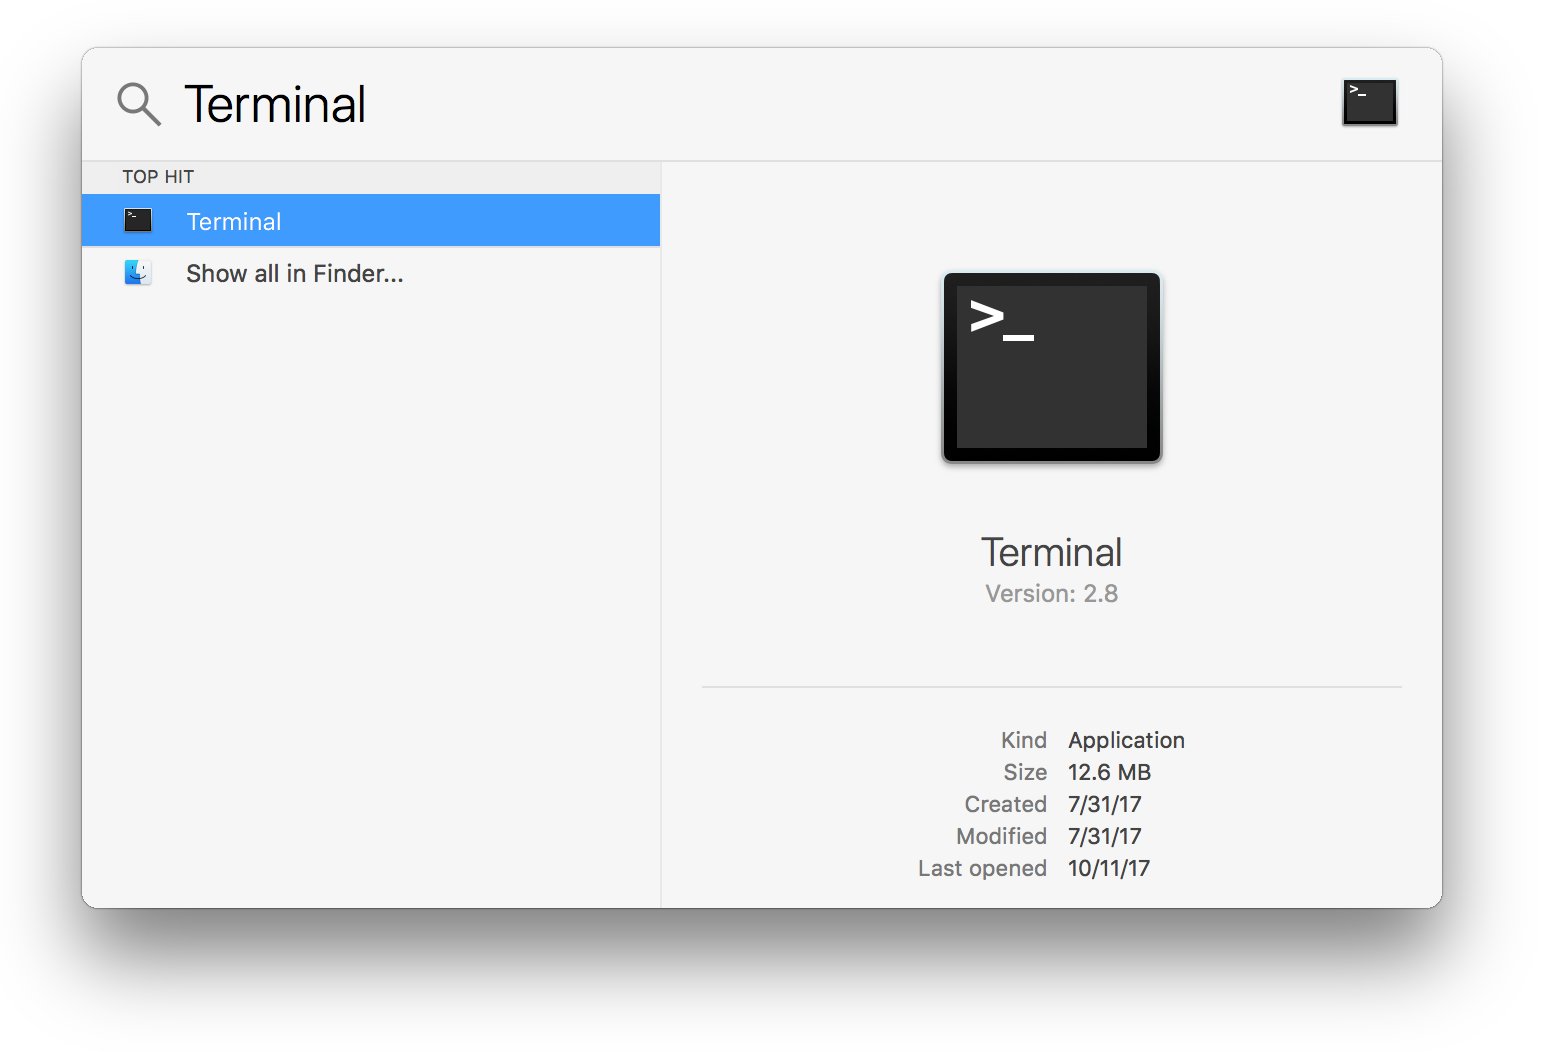
- Once opened, copy and paste one of the following commands, then press Return.
If you aren't sure which to copy and paste, it is safe to do both.
Standalone Version
defaults write com.codeux.apps.textual \
"Off-the-Record Messaging -> Enable Encryption" -bool NO
Mac App Store Version
defaults write 8482Q6EPL6.com.codeux.irc.textual \
"Off-the-Record Messaging -> Enable Encryption" -bool NO
Source material
Original Codeux material preserved from the knowledgebase snapshot of 9 September 2026. Formatting and internal links have been adapted for this site.
Need a hand? Contact us about this guide.